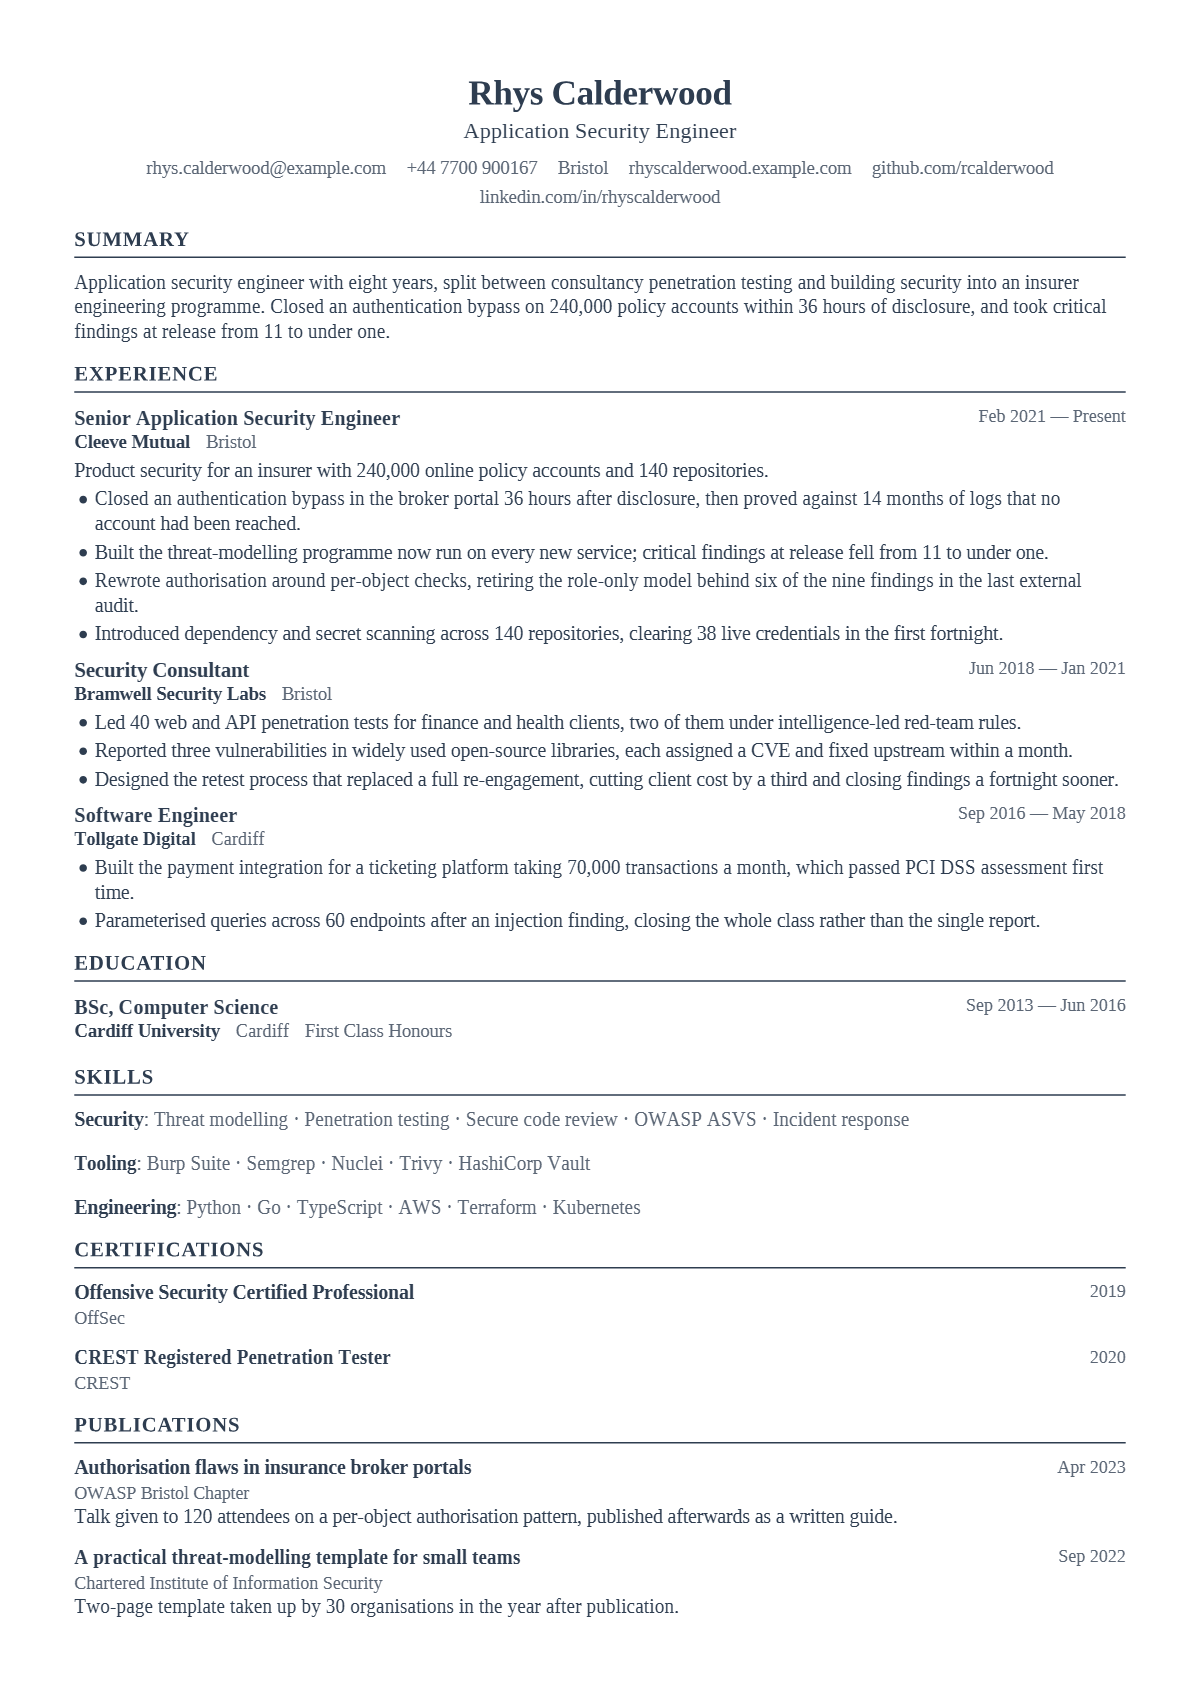
Application Security Engineer résumé example, in the Plainsong design
Eight years of security work, each finding written as the thing it stopped rather than the tool that found it.
Written for United Kingdom, at senior, in the software field, shown in the Plainsong design. Every name, employer, address and number below is invented.
Application security engineer with eight years, split between consultancy penetration testing and building security into an insurer engineering programme. Closed an authentication bypass on 240,000 policy accounts within 36 hours of disclosure, and took critical findings at release from 11 to under one.
Product security for an insurer with 240,000 online policy accounts and 140 repositories.
Closed an authentication bypass in the broker portal 36 hours after disclosure, then proved against 14 months of logs that no account had been reached.
Built the threat-modelling programme now run on every new service; critical findings at release fell from 11 to under one.
Rewrote authorisation around per-object checks, retiring the role-only model behind six of the nine findings in the last external audit.
Introduced dependency and secret scanning across 140 repositories, clearing 38 live credentials in the first fortnight.
Security Consultant, Bramwell Security Labs · June 2018 – January 2021
Led 40 web and API penetration tests for finance and health clients, two of them under intelligence-led red-team rules.
Reported three vulnerabilities in widely used open-source libraries, each assigned a CVE and fixed upstream within a month.
Designed the retest process that replaced a full re-engagement, cutting client cost by a third and closing findings a fortnight sooner.
Software Engineer, Tollgate Digital · September 2016 – May 2018
Built the payment integration for a ticketing platform taking 70,000 transactions a month, which passed PCI DSS assessment first time.
Parameterised queries across 60 endpoints after an injection finding, closing the whole class rather than the single report.
Education
BSc Computer Science · Cardiff University · September 2013 – June 2016
Offensive Security Certified Professional — OffSec
CREST Registered Penetration Tester — CREST
Why this Application Security Engineer résumé works
Findings are written as what was stopped and how fast: an authentication bypass on 240,000 policy accounts closed within 36 hours, then checked against 14 months of logs. That is the incident judgement a senior AppSec hire is tested on.
Fixes are framed by class, not instance. Parameterising queries across 60 endpoints “closing the whole class rather than the single report” shows the engineering habit that separates a security engineer from a tester.
The CV keeps British conventions, “threat modelling”, “authorisation”, a First Class Honours from Cardiff University, which suits the UK employers this sample is written for.
OSCP and CREST Registered Penetration Tester sit beside an OWASP Bristol Chapter talk, so the offensive credentials and the teaching both have outside evidence.
Application Security Engineer résumé: common questions
Which certifications matter on an application security engineer CV in the UK?
CREST registrations are widely asked for by UK consultancies and regulated buyers, and OSCP is recognised everywhere. List the certification name, issuer and year; cloud or secure-coding certificates help when the role is in-house.
How do you write security findings on a CV without sharing sensitive details?
Describe the class of issue, the scale and the response, not the client or the exploit: “an authentication bypass on 240,000 accounts, closed within 36 hours”. Leave out client names unless they are public and keep CVE references to ones already disclosed.
How long should an AppSec engineer CV be?
Two pages is normal in the UK for eight or more years. Spend the space on recent in-house work and the measurable change it made, and keep older consultancy or development roles to two or three bullets each.